Active Directory, security & utilities
Wazuh
Open-source SIEM/XDR across log analysis, intrusion and vulnerability detection.
open sourcecloud + desktop
Independent reference — this page is a review. Wazuh is downloaded from the vendor’s official site, not from here.
| Platforms | Linux server; agents for Windows/Linux/macOS; web; cloud |
|---|---|
| Licence | Open source — GPLv2 |
| Price | Free (self-hosted); paid Cloud |
| Section | Active Directory, security & utilities |
| Updated | 2026-11-05 |
What it is
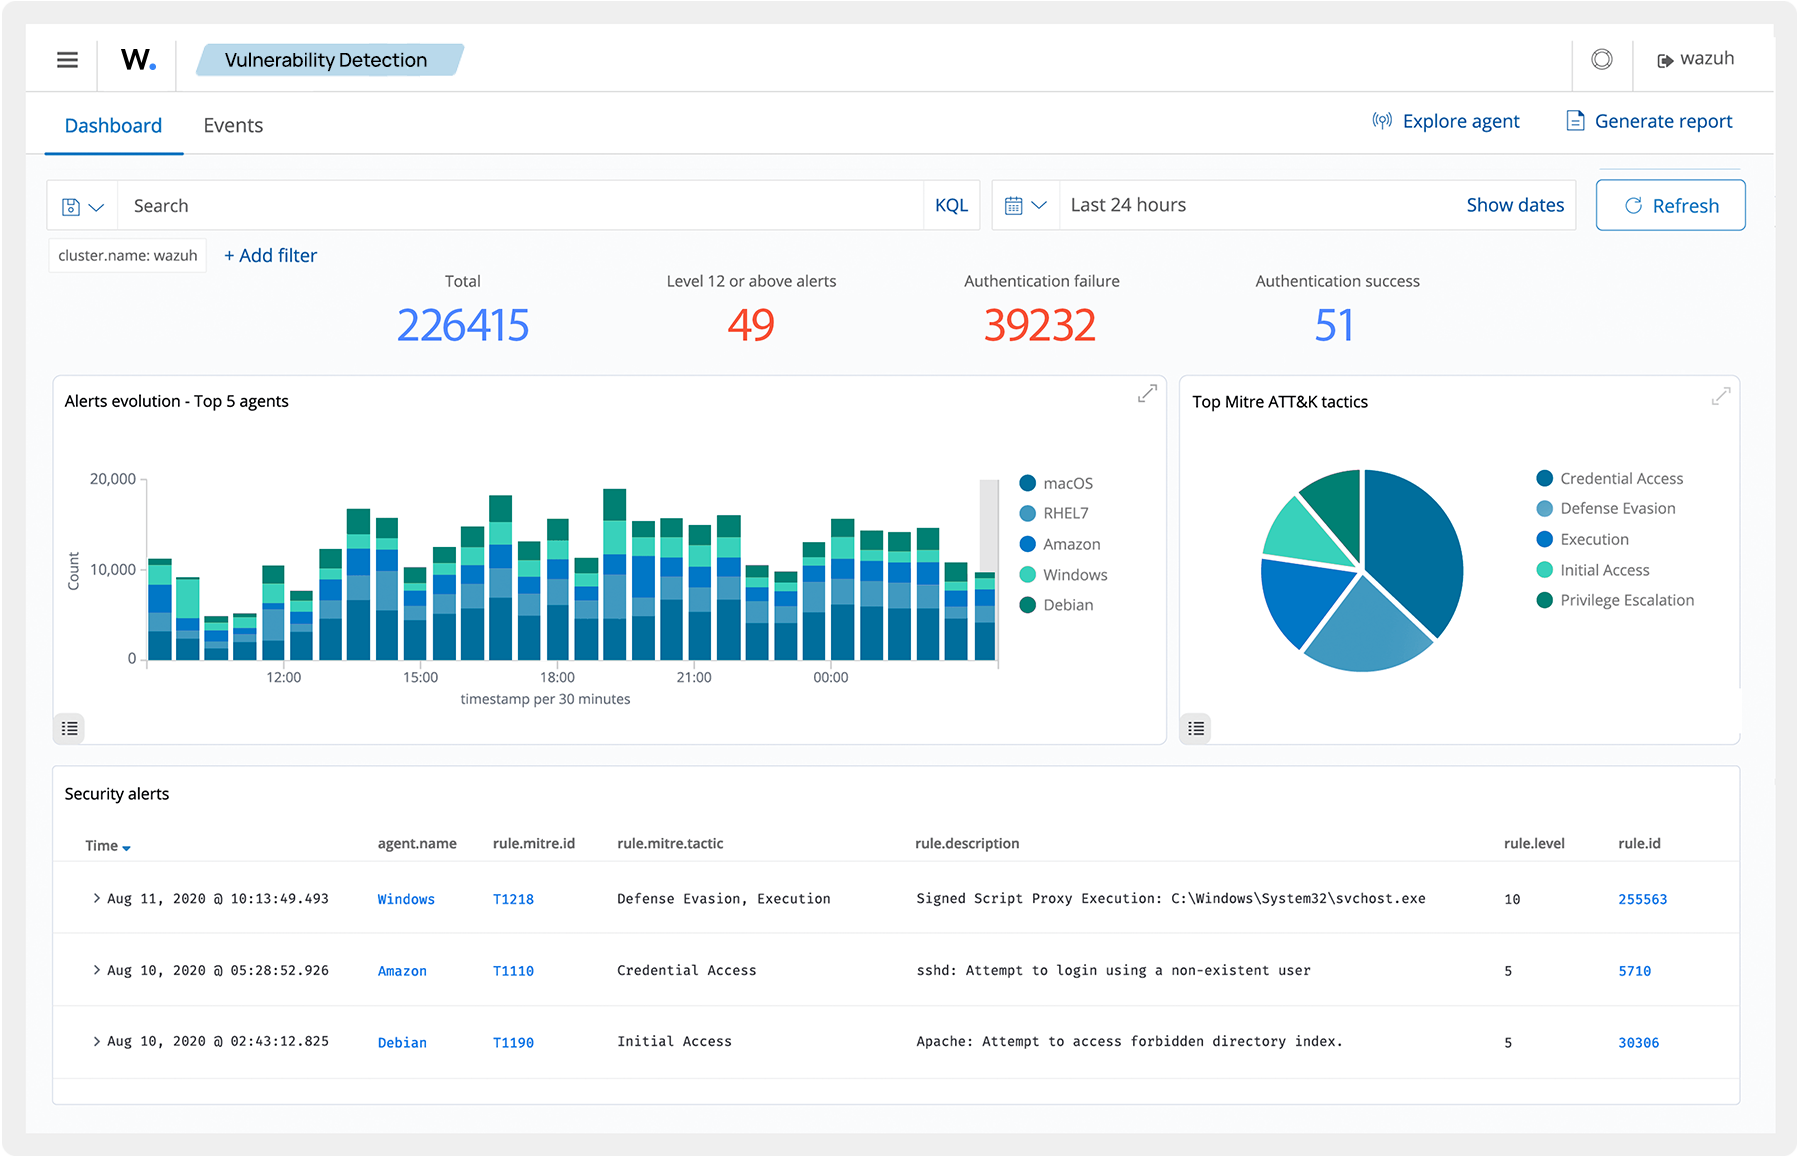
Open-source SIEM/XDR covering security monitoring, log collection and analysis, intrusion detection and vulnerability checks. It watches events across machines, verifies file integrity and supports compliance (PCI DSS, HIPAA) — a free alternative to Splunk.
Problems it closes
- You need SIEM/XDR capability without Splunk-level licensing cost.
- Logs and detections from every host have to be centralised and correlated.
- Compliance (PCI DSS, HIPAA) means file-integrity and policy checks.
How administrators run it
- Push agents out to forward logs and events to the Wazuh server.
- Work the dashboard for detections, file-integrity monitoring and vulnerability data.
- Map alerts against compliance requirements.
Strengths & trade-offs
Strengths
- Free and open source (self-hosted).
- SIEM, XDR, file-integrity and vulnerability detection in one platform.
- Compliance mappings built in.
Trade-offs
- Running and scaling the stack is on you.
- Tuning rules to cut the noise takes effort.
Common questions
Is it free?
Yes — self-hosted and open source. There’s a paid managed Cloud offering too.
Can it replace Splunk?
For many SIEM use cases, yes — a free, open alternative, though Splunk’s ecosystem is bigger.
Alternatives
Nessus (Tenable) Widely used vulnerability scanner — free Essentials for up to 16 IPs. freemiumdesktop Windows/Linux/macOS (local web UI on port 8834) ESET PROTECT Endpoint protection and EDR run from a cloud or on-prem console. paid / trialcloud + desktop Cloud or on-prem console; protects Windows/macOS/Linux + Android/iOS Zabbix Open-source monitoring across servers, network gear, VMs and applications. open sourcedesktop Linux/Unix server, web UI; agents for Windows/Linux/macOS/Unix